SSRF Beyond HTTP: Egress-Path-Incomplete Guards in AI Agent Platforms
A formal egress-path-incomplete SSRF model instantiated on CVE-2026-33234 (AutoGPT). Defines the EPI-SSRF class. Zenodo, 2026.
I build offensive security tooling and break systems. Sixty-two open-source builds, several of them security tools, a live exploit lab, and 14 published CVEs across Apple, CISA, the NSA, NASA, AutoGPT, yt-dlp, and BlueprintUE. This is where the code and the exploits live.
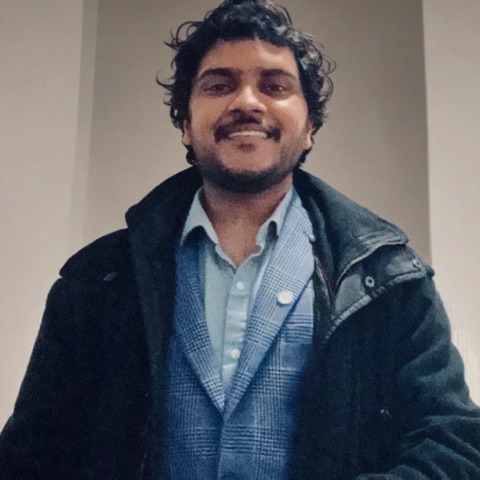
Fourteen published CVEs across Apple, the NSA, CISA, and NASA, AutoGPT, yt-dlp, and BlueprintUE, covering sandbox escapes, SSRF, authentication bypass, IDOR, path traversal, and denial of service.
Credited by CISA in advisory ICSA-26-230-01 for reporting CVE-2026-63133, CVE-2026-63134, and CVE-2026-63177 in CISA Malcolm, and by Apple in macOS security updates.
Browse all CVE advisories → Each CVE has its own page linking the authoritative cve.org record and GitHub Security Advisory.
Live reproduction scripts for disclosed bugs. Each visit loads a random proof of concept, and the tabs switch between them.
Open-access security research preprints with permanent DOIs, indexed by OpenAIRE and listed on Google Scholar.
A formal egress-path-incomplete SSRF model instantiated on CVE-2026-33234 (AutoGPT). Defines the EPI-SSRF class. Zenodo, 2026.
File-write attacks from attacker-controlled archive and download metadata across three 2026 CVEs. Zenodo, 2026.
A static detector for positional permission gaps (the confused-deputy pattern) in AI agent workflows, evaluated by rediscovering four upstream-fixed SSRF CVEs as an independent oracle. Preprints.org, 2026.
Seeding ML-KEM (FIPS-203) from a CHSH-certified quantum source in the QROM. A random-oracle hash carries quantum-conditional min-entropy into IND-CCA security at a one-way-to-hiding loss with no extractor, and classical randomness certificates are shown insufficient. IACR ePrint, 2026.
Benchmarking and analysis of post-quantum cryptography algorithms on constrained IoT hardware. Pace University CYB691 capstone with Ravindra Dholariya.
Independent databases, vendors, government agencies, security media, and community that track, credit, and feature this work. Every link points to the source that carries the credit.
Credits Pavan Nallamothu for CVE-2026-50023 in yt-dlp. Surfaced automatically inside enterprise dependency scans worldwide.
Credited in ICSA-26-230-01 for CVE-2026-63133, CVE-2026-63134, and CVE-2026-63177 in CISA Malcolm.
 CISAICSA-26-230-01 →
Credited in Apple's macOS security release notes for CVE-2026-43763 in Apple Type Services.
 AppleSecurity notes →
Credited reporter on the GitHub-reviewed advisory for the yt-dlp filename bug, GHSA-c6mh-fpjc-4pr3.
Google's open vulnerability database mirrors the credited advisories into automated supply-chain tooling.
Apple's advisory APPLE-SA-07-27-2026-3 on the Full-Disclosure mailing list credits Pavan Nallamothu by name for CVE-2026-43763.
 Full-DisclosureAPPLE-SA-07-27-2026-3 →
Independent coverage of CISA ICSA-26-230-01 that credits pavanchow among the researchers who reported the Malcolm findings.
 OT Security WireRead →
Independent write-up naming pavanchow as the reporter of CVE-2026-63133, CVE-2026-63134, and CVE-2026-63177 to CISA.
 CyberICTRead →
First non-government site to credit pavanchow for the CISA Malcolm advisory ICSA-26-230-01.
 Assurant CyberRead →
Featured as a SECON NJ 2024 organizer and speaker on Zero Trust, with a full-name researcher bio in the chapter newsletter.
 ISC2 NJNewsletter →
Credits Pavan Nallamothu for CVE-2026-65412, a null pointer dereference in CoreText reachable by processing web content, and separately names him under Additional recognition for Foundation in the same release.
AppleAdvisory 149034 →Independent coverage of every security fix in iOS 27 and iPadOS 27 that carries Apple's credit lines verbatim, including the CVE-2026-65412 CoreText entry and the Foundation acknowledgment.
 9to5MacRead →
The project's own SECURITY.md names Pavan Nallamothu in section 13, Acknowledgments, for one advisory. The disclosure record held by the maintainers themselves.
 SECURITY.mdAcknowledgments →
Apple's macOS Sonoma 14.8.8 advisory on the Full-Disclosure list credits Pavan Nallamothu and Jared Reyes for CVE-2026-43763, a sandbox file-read in Apple Type Services.
 Full-DisclosureAPPLE-SA-07-27-2026-4 →
A long-running archive of vulnerabilities, advisories, and exploits. File entry 230694.
 Packet StormFile 230694 →
Credits Pavan Nallamothu in the AIT-Core security advisory for a format-string memory exhaustion in the BSC capture manager, reachable through an unvalidated file name pattern and capable of crashing the ground station capture manager. Fixed in 3.1.2.
 NASA AMMOSGHSA-fjr5-6w4j-47xf →
Running AWS infrastructure at scale, building and hosting CTF challenges, and supporting a university campus.
Master of Science in Cybersecurity from Pace University, awarded a Graduate Merit Scholarship.
Pace University, New York, NY · 2023 - 2025 · Graduate Merit Scholarship
Talks, mentoring, competition, and event organizing across the security and open-source communities.
Sixty systems tools written from scratch in Rust, each its own repository with a live project page. Build-your-own versions of the software I break for a living, grouped from compilers and kernels to databases, browser engines, and security tooling.
A compiler that lexes, parses, and lowers a small language to stack bytecode, then runs it on a bundled VM.
A compiler backend that lowers SSA to a target machine with graph-coloring register allocation.
A small statically-typed language with type inference, built from a lexer, parser, and checker.
A dynamically typed language with a bytecode compiler and a stack-based virtual machine.
A small bytecode virtual machine with its own instruction set, a text assembler, and a runner.
A tiny embeddable scripting language with a one-pass lexer, recursive-descent parser, and tree-walking interpreter.
A compiler optimizer with a readable pass pipeline: constant folding, propagation, and algebraic simplification.
A CHIP-8 emulator with a fully unit-tested CPU core covering the full opcode set.
An amnesic aarch64 kernel that runs entirely in RAM, encrypts its vault in memory, and wipes every secret on exit.
A from-scratch virtual CPU, assembler, and preemptive OS kernel you can boot in the browser.
A CPU scheduler running FIFO, SJF, round-robin, priority, and MLFQ over real processes.
A rootless Linux container runtime that isolates a process with namespaces, pivot_root, and dropped capabilities.
A Unix shell with a hand-written tokenizer, pipeline parser, and process wiring for pipes and redirects.
A deterministic RTOS simulator on an emulated microcontroller, with a preemptive scheduler and priority inheritance.
A readable memory allocator that plugs in as a global allocator and exposes live stats.
A deterministic boot sequence simulator with an MBR parser and boot config, zero dependencies.
A deterministic type-1 hypervisor simulator that runs several guest VMs.
A dependency-free tiling window manager engine, zero external crates.
A deterministic microkernel simulator providing threads, address spaces, and synchronization.
A from-scratch scripting sandbox that runs untrusted code under resource limits.
ChaCha20-Poly1305 authenticated encryption from scratch, proven against the RFC 8439 test vectors.
An auth server with HMAC-SHA256 signed tokens and salted password hashing, no crypto crates.
A from-scratch proof-of-work blockchain whose only primitive is SHA-256.
A static analyzer whose result is the data-flow path from an untrusted source to a dangerous sink.
A query language whose results are attack paths across identity and network graphs.
An EVM bytecode disassembler that reconstructs intent and flags dangerous opcodes.
A zero-knowledge proof system built from scratch with no crypto crates and no elliptic curves.
A layer 7 reverse proxy and load balancer with health checks, circuit breaking, outlier ejection, and retries.
A load balancer with round-robin, weighted round-robin, least-connections, and seeded random strategies.
An HTTP server built from scratch on std::net, no hyper and no web framework.
A browser engine with an HTML parser, a CSS parser, the cascade, block layout, and paint.
A browser rendering engine that runs HTML and CSS through parse, layout, and paint.
A programmable single-binary reverse proxy where routing rules are a compiled DSL, not YAML.
A message broker with topics, wildcard subscriptions, and bounded per-subscriber queues.
A length-prefixed framing codec plus a small typed request/response protocol over TCP.
A from-scratch API gateway where routing, auth, and rate limiting are a pure pipeline.
A distributed file system with quorum writes, self-healing, and content-addressed chunks.
A from-scratch PostgreSQL driver that speaks the v3 wire protocol over TCP with hand-written SCRAM-SHA-256.
An LRU cache with TTL expiry, a capacity bound, and live stats.
An embedded single-binary key-value store, a persistent append-only log with an in-memory index.
A durable, ordered, embedded key-value store written from scratch.
An embedded relational database with a real SQL subset, a hand-written lexer, parser, and executor.
A file system that lives inside one container file, with a superblock, a bitmap allocator, inodes, and directories.
A tiny content-addressed version control system with blobs, trees, and commits.
A full-text search engine with an inverted index and TF-IDF ranking.
A dependency-free 2D game engine with an ECS, a fixed-timestep loop, and impulse-based physics.
A dependency-free retained-mode GUI layout engine that lays out a tree of widgets.
A 2D physics engine with semi-implicit Euler integration, circle collision detection, and impulse resolution.
A software rasterizer that draws real 3D triangles on the CPU, no GPU.
An audio synthesis project with oscillators, an ADSR envelope, mixing, and a hand-written WAV writer.
A neural network with a reverse-mode scalar autograd engine and a tiny MLP, trained on XOR.
A dependency-free code-intelligence engine with go to definition, find references, live diagnostics, and safe rename.
A portable time-travel debugger that steps backward through a running program.
A single-binary cron scheduler with a pure, unit-tested schedule engine you can embed.
A from-scratch package manager whose core is a PubGrub dependency resolver that explains conflicts.
A dependency-free editable text buffer backed by a piece table.
A deterministic Raft consensus simulator showing leader election, terms, and log replication.
A from-scratch CI/CD engine whose scheduler is a pure, deterministic DAG executor.
A dependency-free, Kubernetes-style reconciliation control loop that schedules pods onto nodes.
A profiler with a call tree of self time and total time, rendered as a chronomandala.
A Claude Code subagent and MCP server that reads a repository and ships a living architectural map of it.
A website security scanner that grades a site A through F on security headers, cookie flags, exposed files, TLS configuration, mixed content, and subdomain-takeover risk.
Type help to see all commands. Try neofetch, cves, experience, or scan github.com.
Reach out for collaboration, coordinated disclosure, or a conversation about offensive security.
Have a question or want to work together? Reach out directly.
Connect with Pavan Nallamothu on LinkedIn.
Just kidding. But you did type the Konami Code!
 Snyk
 OSV